
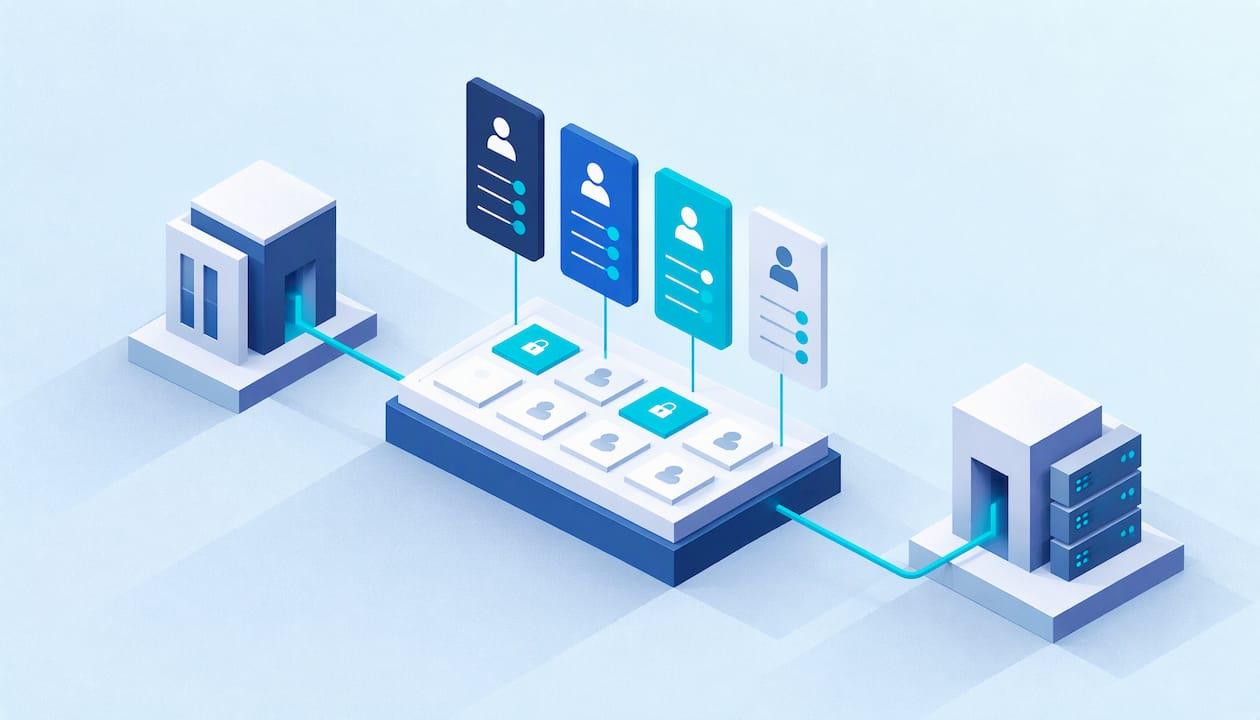
Role-based permissions give people access to a system through their job role instead of one person at a time. You define what each role can see and do, then assign people to roles. The formal name is role-based access control (RBAC), and it is the default way business software decides who can open an invoice, edit a schedule or change a setting. This guide explains how it works, how to set it up step by step, and what a sensible role set looks like for a mobile detailing business with a few vans and an office.
TL;DR
- Role-based permissions attach access rights to roles (technician, scheduler, billing), and people get access by being assigned a role.
- Setup is three moves: define permissions, group them into roles, assign roles to users. Then review them on a schedule.
- Start from the tasks people actually do, and give each role the minimum it needs.
- RBAC suits small and simply structured teams well. Add context-based rules only when roles multiply or locations and turnover grow.
- For a detailing shop, the lines that matter most are money (invoices, payments), customer data and system settings.
Table of Contents
- What role-based permissions are
- How role-based access control works in practice
- Why small businesses use it
- How to set up role-based permissions step by step
- A sample role set for a mobile detailing business
- Keeping permissions current
- Where role-based permissions run out
- Our perspective
- Run your detailing business from one system
- FAQ
- Sources
What role-based permissions are
In an RBAC system, an administrator assigns each user one or more roles, and each role represents a set of permissions. IBM describes RBAC as authorizing access to systems, applications and data based on a user's predefined role. Three basic rules sit underneath: a user must be assigned a role, the role must be authorized for that user, and the permission must be authorized for that role.
The idea is not new. NIST's RBAC project documents a general-purpose RBAC model proposed in 1992 by Ferraiolo and Kuhn. It was presented as an alternative to the older discretionary and mandatory access control models. The model was later formalized as a U.S. standard, ANSI/INCITS 359-2004.
The practical payoff is simple. When a new technician starts, you do not tick forty boxes. You assign the Technician role. When someone changes jobs, you swap the role. When an auditor, an insurer or a nervous owner asks who can see customer payment details, you have one short list to read instead of a spreadsheet of exceptions.

Roles, permissions and users: the vocabulary
The ANSI/INCITS standard defines core RBAC through a handful of elements: users, roles, objects, operations and permissions. In plain terms:
| Term | What it means | Detailing example |
|---|---|---|
| User | A person (or account) that signs in | A technician named Marcus |
| Role | A job-shaped bundle of permissions | Technician, Scheduler, Billing |
| Object | The thing being protected | A job, an invoice, a customer record |
| Operation | What can be done to it | View, create, edit, delete, export |
| Permission | An operation allowed on an object | "Edit invoice" |
Users are assigned to roles, and permissions are assigned to roles. Users never get permissions directly. That one rule is what keeps the system tidy.
How role-based access control works in practice
Auth0 boils enforcement down to three logical steps: define permissions, assign permissions to roles, assign roles to users. When a person signs in, the system looks up their roles, collects the permissions those roles carry, and allows or blocks each action accordingly.
In modern web and mobile apps the same logic often travels in a signed token. According to Auth0's guide, the identity provider works out the user's roles and permissions and issues a JWT access token with those claims. The backend then checks the claims before it allows a request. That is why a block on invoices holds even if a technician somehow learns the web address of an invoice page: the check happens on the server, not just in the menu.
The architecture behind it
If you have seen the phrase "structure of RBAC architecture," there are two answers, one for standards readers and one for builders.
The standard answer: the ANSI/INCITS 359-2004 reference model has four components. They are Core RBAC, Hierarchical RBAC (senior roles inherit from junior ones), Static Separation of Duty and Dynamic Separation of Duty. Separation of duty simply means two sensitive powers should not sit with one person, such as creating a refund and approving it.
The academic answer: a three-tier reference architecture from Sandhu and colleagues describes multiple user views, a single unified community view for administration, and multiple implementation views where each subsystem enforces the rules. For a small business, the takeaway is modest: someone owns the master list of roles, and every tool you use should follow it.
Why small businesses use it
Controlling access through roles reduces the administrative burden for security managers and improves auditing, according to NIST's role engineering publication. Okta's developer documentation makes the same point from the audit side: once a consistent framework exists, the question "who has access to what?" gets much easier to answer.
For a detailing business the benefits are concrete:
- Fewer billing mistakes. Only the people who handle money can edit invoices or refund payments.
- Customer privacy. A technician on a van needs the address and vehicle notes for today's job, not your whole customer list.
- Faster onboarding and offboarding. Hiring a seasonal helper or letting someone go takes a minute, not an afternoon.
- Fewer accidents. Nobody deletes a recurring schedule or changes pricing by clicking the wrong thing.
How to set up role-based permissions step by step
There is no single correct sequence, but the vendor guidance converges. Tenable's best practices guide recommends seven steps: plan the access model, create tags, create user groups (optional), create users, create permission configurations, assign permissions, and validate access. For a small business, that compresses into five.
- List what the system holds. Customers, vehicles, jobs, photos, invoices, payments, pricing, reports, settings, integrations.
- List what people actually do. Take calls, book jobs, drive routes, detail vehicles, send invoices, reconcile deposits, run reports.
- Give each job the minimum it needs. For every task ask: what breaks if this person cannot do it? If nothing breaks, remove the permission.
- Group tasks into roles and name an owner. One person (usually you) approves who gets each role.
- Assign, then validate. Sign in as a test user in each role and confirm that allowed actions work and blocked ones really are blocked.
One caution from the research: implementations that only check role membership, without tying roles to specific permissions, oversimplify RBAC. Roles that are just labels on groups of people are not much protection. Each role should map to named permissions on named objects.
Top-down or bottom-up
NIST's role engineering paper describes a top-down approach in which functional stakeholders or subject-matter experts, with a facilitator, identify role names and attach permissions to them. In a detailing company, that is you and your lead technician sitting down for an hour with a list of tasks. It beats copying a template, because your shop's real workflow decides the roles.
A sample role set for a mobile detailing business
The following is our suggested starting point, built from the logic above rather than from any one product's settings. Adjust it to your headcount. A solo detailer may be every role at once and still benefit from thinking in roles, because it shows what to hand off first when you hire.
| Role | Can do | Should not do |
|---|---|---|
| Owner / admin | Manage users, integrations, pricing and settings | Work daily under the same login used for admin tasks |
| Scheduler / dispatcher | View and reassign jobs, see customer address and contact info, manage routes | See payment details or export the customer list |
| Technician | See assigned jobs, job notes, checklists; upload photos | Browse all customers, edit pricing, see invoices |
| Billing / bookkeeper | Create invoices, record payments, run aging reports | Change lead sources, schedules or user access |
| Sales / estimator | Own leads and quotes, view history for their own accounts | See other reps' pipelines or manage users |
| Manager | Run reports across vans, approve role requests | Change security settings |
A few notes on why the lines fall where they do.
Technicians see today, not everything. A van crew needs the address, vehicle details, service package, intake notes and a place to add photos. Our posts on photo documentation that maps to your CRM and one-page intake with VIN, mileage and eSignatures cover what that capture flow can look like.
Schedulers control the calendar, not the cash. Once you run more than one van, someone assigns and reshuffles jobs every day. See multi-van scheduling and round-robin job assignment for how the work gets divided. That person needs addresses and contact details to dispatch, but rarely needs card or bank information.
Billing is its own lane. Whoever invoices should not also be the person who edits the schedule, and vice versa. If you take bank transfers, the walkthrough on accepting ACH payments shows the money side that this role touches.
Specialists get specialist access. A technician who also services vehicle drivetrains follows documented procedures, the kind laid out in guides like AWD system service best practices. In your system, that person's role still stays limited to the jobs assigned, with the technical detail living in job notes rather than in wider system access.
Mapping roles to a growing shop
| Stage | Typical roles | What to do |
|---|---|---|
| Solo | One person, all hats | Use a separate admin login from the one used daily in the field |
| 2 to 4 vans | Owner, lead tech, technicians | Split Technician from Owner first; add a Scheduler when dispatch eats your day |
| Multi-van or franchise | Owner, managers, schedulers, billing, technicians | Add Billing and Manager roles; require approval for new role requests |
The order matters. The first split most detailers need is between the person who owns the business and the people who work jobs. The second is between whoever sets the schedule and whoever handles payments.
Keeping permissions current
Setting up roles is a day's work. Keeping them accurate is the part that matters over a year. Governance guidance from the research points to a few habits that scale down well:
- Review access quarterly. Print or export who has which role and confirm each one with the role's owner.
- Tie changes to events. Hire, promotion, van reassignment and departure each trigger a role change the same day.
- Give every role an owner. That person approves who gets it.
- Watch the number of roles. If you have more roles than you have people, something has gone wrong.
- Follow the standards where they apply. CIS Controls v8 Safeguard 6.8 calls for roles tied to job functions, access assigned through those roles rather than user by user, and roles kept current as responsibilities change, as summarized here.
Two habits matter most for a small crew. First, do not share logins. A shared technician login erases the audit trail that roles are meant to give you. Second, do not create one-off exceptions that never expire. If a helper needs temporary access to invoices, put a reminder on the calendar to remove it.
Where role-based permissions run out
RBAC is widely used, and it is a good fit when access follows job duties. Okta's identity guidance says it works best for small or simply structured workgroups where access is defined by job duties. It adds that many organizations use a hybrid, with RBAC for high-level access and attribute-based rules for fine-grained controls.
The known stress points, according to NIST's paper Adding Attributes to Role-Based Access Control, are the effort of setting up the first role structure and limited support for dynamic conditions such as time of day. KuppingerCole's 2026 analysis likewise says RBAC remains the most popular model but is increasingly strained by real-time decisioning and scale. InfoQ puts the threshold for moving beyond flat RBAC at the organizational level: many services making access decisions, ownership that must be re-verified, and an audit obligation with teeth.

For a detailing business, that means you are comfortably inside RBAC territory. Signs you may be pushing its edges are a franchise with many locations, each with its own rules, or constant one-off exceptions such as "this technician can see invoices, but only for his own jobs, and only this week." At that point, you add conditions on top of roles, instead of creating a new role for every exception.
Our perspective
We built Mobile Detail AI because detailing businesses run on trust. Customers hand over their keys, their addresses and their payment details, and the person on the van should never have to wonder how much of the business they are allowed to see.
Our view is that permissions should follow the way a detailing business actually works. A technician needs the day's jobs, vehicle notes and a way to add photos. A scheduler needs the calendar, routes and customer contact details. Whoever bills needs invoices and payments. The owner needs the whole picture. When those lines are clear, you can add a van or hire a scheduler without handing over the keys to everything.
That is why we pair the tools a detailer needs day to day, including visual scheduling, route optimization, customer management, invoicing and business analytics, in one place. When scheduling, customers, vehicle history and payments live together, it is far easier to decide who should touch which piece than when they are scattered across texts, spreadsheets and a card reader.
Our advice to every detailer, solo or multi-van: write your roles down before you hire, name who approves access, and review the list every quarter.
Mobile
Run your detailing business from one system
If you are a detailer ready to bring scheduling, customers, invoicing and payments into one place, Mobile Detail AI's provider plans are listed at our subscription page. The CRM-Only plan is $1 per month, the Marketplace plan is $59 per month, and the Preferred plan is $139 per month. Multi-van owners and franchises can also start with our guide to piloting fleet detailing management using three real vehicles.
Car owners looking for a vetted detailer can browse services such as interior, exterior, ceramic coatings and paint correction on our Discover page.
FAQ
What is an example of role-based access control?
A technician role can see only the jobs assigned to them, add notes and upload photos. A billing role can create invoices and record payments but cannot change the schedule. The owner role manages users and settings. Each person gets one role, and the role decides what they can do.
How do you assign roles in an RBAC system?
First define the permissions, such as view job or edit invoice. Next group them into roles, then assign each user the role that matches their job. This is the three-step sequence Auth0 describes. Afterward, sign in as a test user in each role to confirm the limits work.
Is RBAC still used?
Yes. Permit.io's 2025 survey found that 86.6% of developers say RBAC is the model their platform uses today. Larger organizations often layer attribute-based or relationship-based rules on top of it. For a small or mid-sized service business, roles alone usually cover what you need.
What is the difference between a role and a permission?
A permission is a single allowed action on a single object, such as editing an invoice. A role is a named bundle of permissions that fits a job, such as Billing. You assign roles to people, so you manage a handful of roles instead of dozens of individual settings.
Sources
- IBM: What Is Role-Based Access Control (RBAC)?
- NIST CSRC: Role Based Access Control FAQs
- ANSI/INCITS 359-2004: Role Based Access Control
- Auth0: What is Role Based Access Control (RBAC)?
- Sandhu et al.: A Three Tier Architecture for RBAC
- NIST: Role Engineering: Methods and Standards
- Okta Developer: Role-Based Access Control
- Tenable RBAC Best Practices Guide
- EmpowerID: Enterprise Authorization whitepaper
- CIS v8 Safeguard 6.8 guide
- Okta: RBAC vs. ABAC
- NIST: Adding Attributes to Role-Based Access Control
- KuppingerCole: Authorization Put to the Test
- InfoQ: Identity as an Architectural Concern
- Permit.io: The State of Authorization 2025